Request a walkthrough
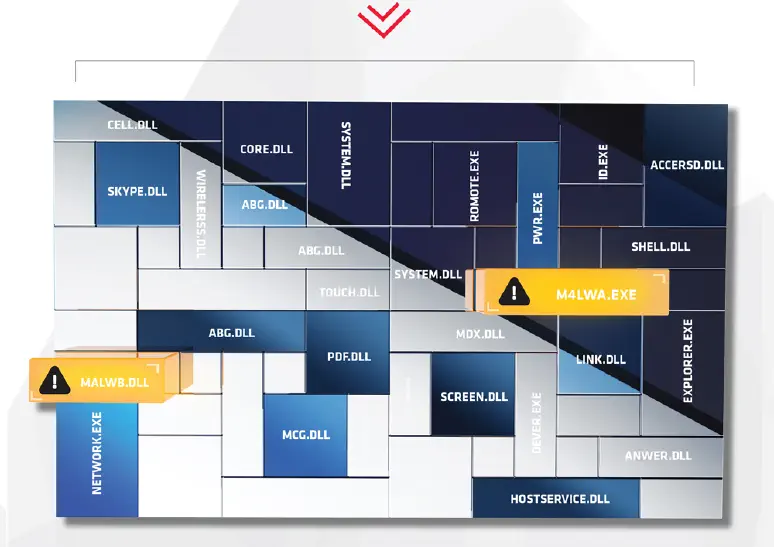
SNOW combines Arc4dia’s proprietary telemetry with other evidence and intelligence to support live threat hunting, investigation and authorized action on running systems. Live forensic analysis also helps uncover evidence of earlier compromises.

Raise leads from suspicious behaviour, memory anomalies and covert execution indicators.

Follow relationships over time, from remote access and observed AI-tool activity to processes and network connections.
Use the investigation to guide authorized response with your security team. Human review and response arrangements are agreed for each engagement.


Keep context across processes, AI-tool activity and network relationships, wherever the evidence supports the link.

Investigate in-memory anomalies and covert execution alongside the activity visible on disk.

Put observed activity in context with public exposure records and threat intelligence.

Gather the next piece of evidence and coordinate response within the permissions and scope agreed with your team.
Coding agents launch shells, run scripts and interact with developer workflows. SNOW’s AI-agent module goes beyond recognizing a tool process: it groups observed activity into work sessions and keeps process lineage in context over time.
Relate that activity to the wider investigation, including remote access, child processes and network connections where the records support those links. Recognizing an AI tool is not the same as deciding its activity was approved.


Review investigations, relationships and available evidence in SNOWboard. Endpoint-level detail depends on enrolled hosts and their telemetry; external intelligence keeps its own source and observation date.